Weglot and PHP2Shell: What Weglot Users Need to Check Now
Short answer: Parts of Weglot's infrastructure run on PHP. According to Weglot, the PHP2Shell vulnerabilities were patched on October 21, 2026 at around 7 pm CEST, with additional firewall rules in place from around 3 pm. Weglot's Customer Success team confirmed this to us in writing on October 22. If you use the Weglot WordPress plugin, however, that alone is not enough. The plugin runs on your own server, and your hosting provider has to update the PHP on that server.
A note on timeliness: PHP2Shell is a breaking story. New information keeps coming in. This article reflects the situation as of October 23, 2026 and may soon be out of date. The official sources always take precedence. That is why every screenshot shows its date and time.
Is Weglot Affected by PHP2Shell?
Weglot uses PHP in parts of its infrastructure and therefore had to act. PHP2Shell affects every PHP installation that handles web requests, as explained in our article PHP Security Vulnerability PHP2Shell. Up to October 23, we could not find a public statement from Weglot, neither on its blog nor on the Weglot status page. So we asked Weglot directly on October 22. The Customer Success team replied the same day:
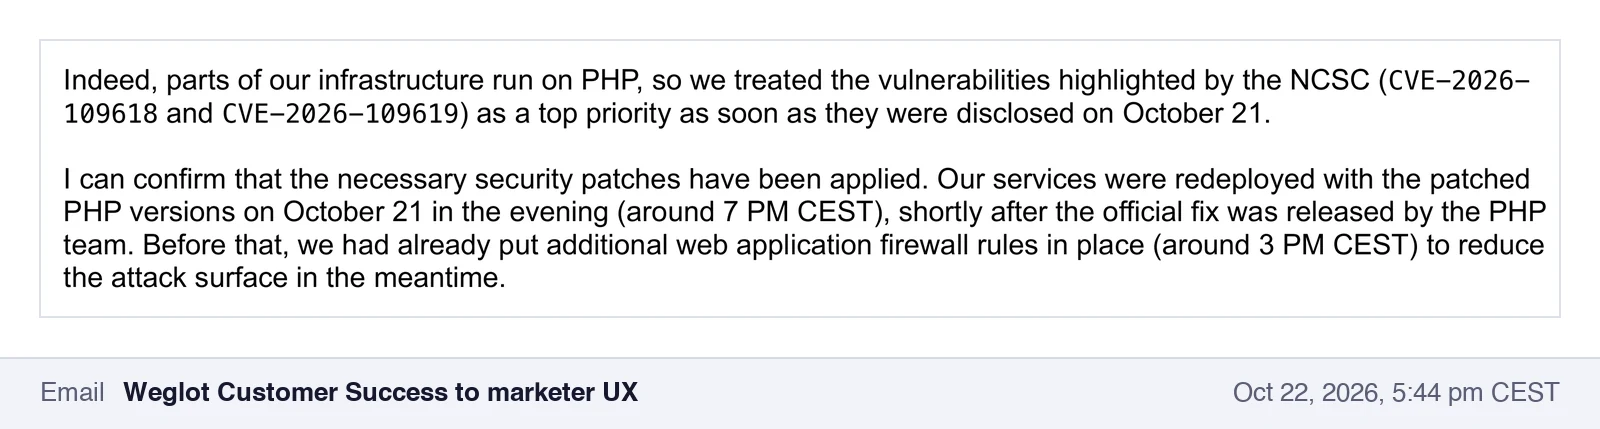
In summary:
- Parts of Weglot's infrastructure run on PHP.
- Weglot treated CVE-2026-109618 and CVE-2026-109619 as a top priority from the moment they were disclosed on October 21.
- At around 3 pm CEST, Weglot put additional web application firewall rules in place to reduce the attack surface until the patch.
- At around 7 pm CEST, Weglot's services were running on the patched PHP versions, shortly after the PHP team released the fix.
That means Weglot responded on the day of disclosure. Two of our questions were not explicitly answered: whether there were any signs of exploitation before the patch, and whether customers need to do anything themselves. As soon as Weglot publishes more on this, we will add it here.
How Weglot Is Set Up Decides What You Need to Do
People searching for "Weglot PHP" usually want to know whether their own website is exposed through Weglot. That depends on how Weglot is integrated on your site. There are three ways, and each one means something different.
1. Language versions on subdomains or subdirectories
Many Webflow websites use this setup. For each language, a DNS record such as fr.your-company.com points to Weglot's servers. When someone opens the French page, the Weglot Reverse Proxy fetches the original page from your server, has it translated through the Weglot API and delivers it. That is how Weglot describes it on its page "How Weglot technically works".
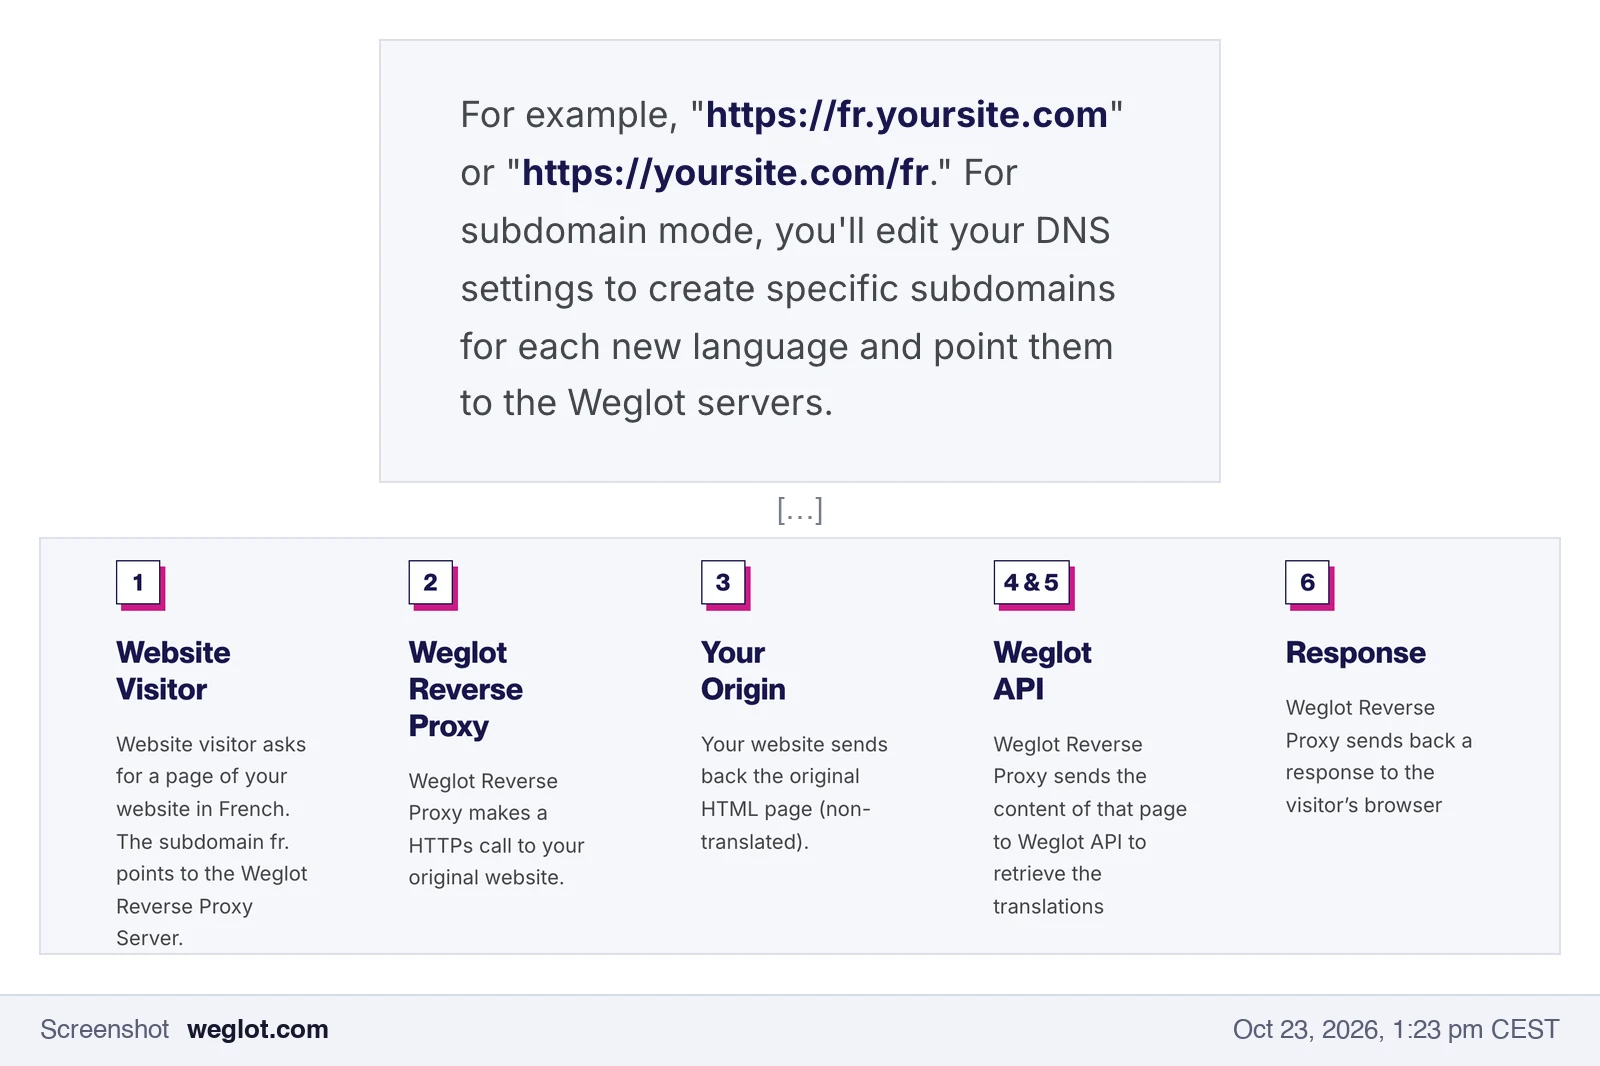
So the translated pages come from Weglot. Weglot did not say which of these parts run on PHP. According to Weglot, however, its services have been running on the patched PHP versions since the evening of October 21. Your original website is a separate question. If it runs on PHP, for example on WordPress, it has to be updated too. If it runs on Webflow, it is not affected, which Webflow has confirmed officially (Webflow and PHP2Shell).
2. The Weglot WordPress plugin
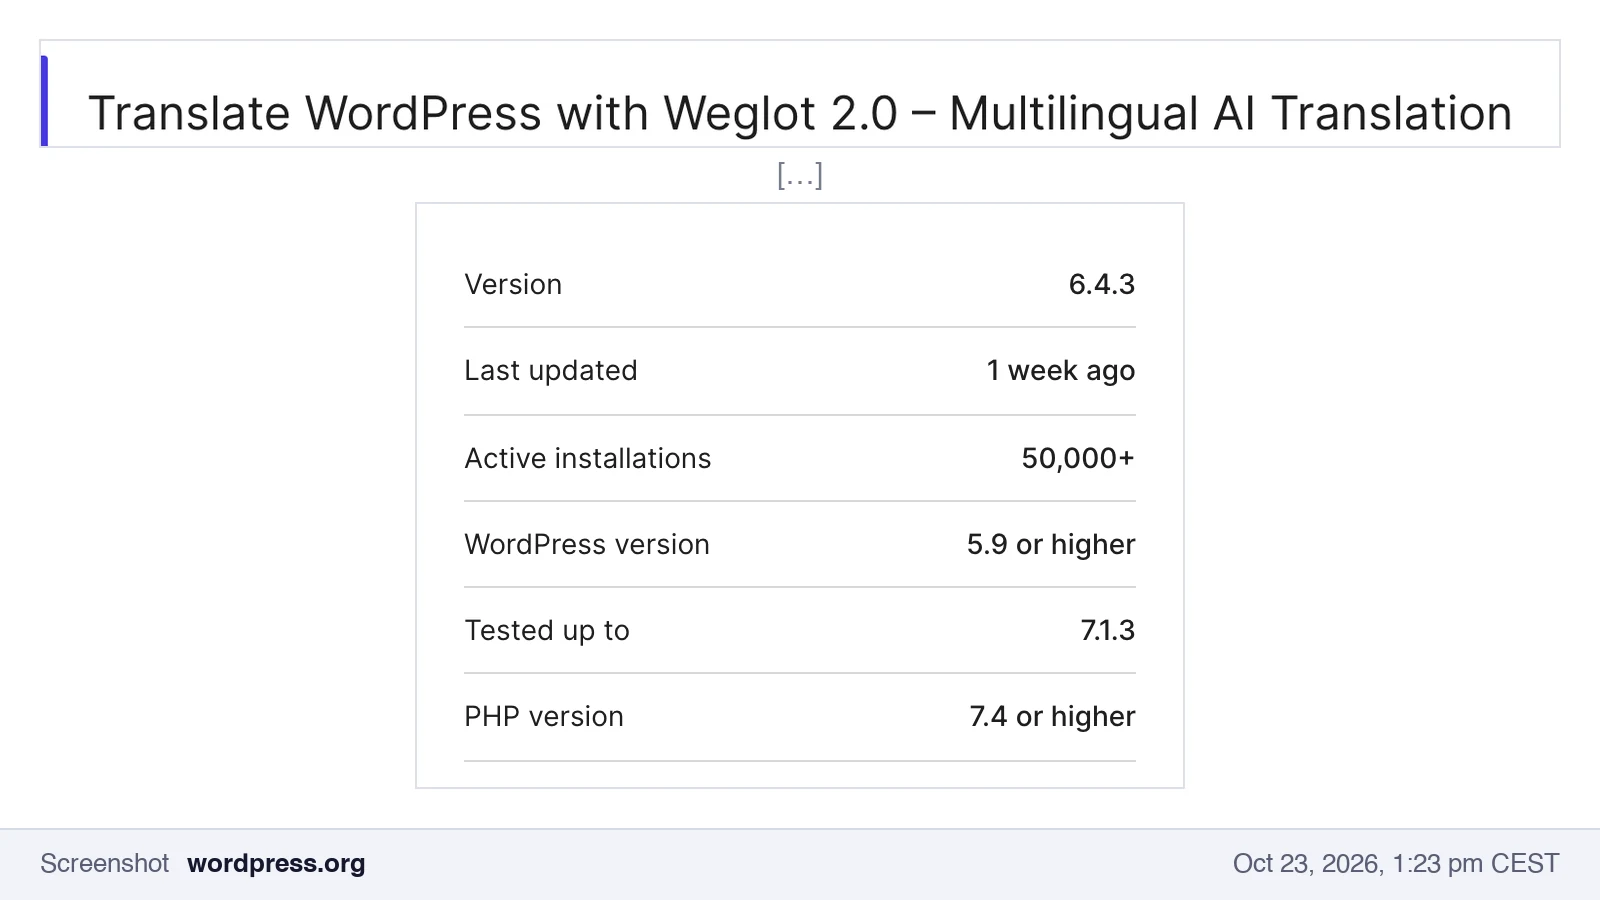
On WordPress, Weglot is usually added through the plugin "Translate WordPress with Weglot". According to wordpress.org, it has more than 50,000 active installations and requires PHP 7.4 or higher. Like every WordPress plugin, it is PHP code that runs on your own server. The translations themselves are stored on Weglot's servers.
This is the most important point of this article: Weglot's patch does not protect your WordPress server. PHP2Shell sits in PHP itself, not in the plugin. Updating the Weglot plugin or WordPress therefore does not close the vulnerability. Your hosting provider has to update PHP on your server to 8.2.35, 8.3.36, 8.4.27, 8.5.12 or later. PHP 7.4, 8.0 and 8.1 no longer receive regular releases. If your server still runs one of these versions, it is time to move to a supported version (security advisory on php.net).
3. JavaScript snippet only
The simplest integration is a script that you paste into your site. Weglot itself calls it the fastest way to get started, for example for testing. In this setup, no Weglot code runs on your server. For PHP2Shell, all that matters is what your website itself runs on.
What about Weglot's PHP library?
Packagist still lists the package weglot/weglot-php, a PHP library for the Weglot API. Its last release, 1.1.6, dates from February 23, 2021, and the GitHub repository is no longer available. If you still use this package in a project of your own, you are running PHP on your own server and have to update it there as well.
How to Check Your Weglot Setup
- Find out how Weglot is integrated. In the Weglot dashboard, the Setup page shows whether you use subdomains or subdirectories (Weglot help on DNS). On WordPress, the installed plugin tells you.
- WordPress with the Weglot plugin: check PHP with your hosting provider. What matters is the PHP version actually running, not the one selected in the control panel. Versions patched against PHP2Shell are 8.2.35, 8.3.36, 8.4.27 and 8.5.12 or later.
- Subdomains or subdirectories: check your original site. According to Weglot, its servers are patched. Your original pages, however, still come from your own server. If they run on PHP, step 2 applies to them as well. If they run on Webflow, they are not affected.
- Do not forget older projects. If an older project still uses the weglot/weglot-php library or an old WordPress installation with Weglot, that server belongs on your list.
- Follow the PHP team's update. Since October 23, the PHP team additionally recommends setting "session.upload_progress.enabled=0" until the next regular release (notice on php.net). This applies to your own PHP server.
Important: These five steps give you a first overview. They do not replace a professional security review. Have your setup checked by a professional now, for example your hosting provider, your IT service provider or us. That is the only way to be truly on the safe side.
What This Case Shows
Weglot responded on the day of disclosure, with firewall rules in the afternoon and the patch in the evening. That is fast. But the case also shows that every service involved in delivering your website is a separate system whose security is not in your hands. If a service does not get in touch on its own, ask. We did exactly that on October 22 for our clients' projects, with Weglot as well as with hosting providers and other services.
With Webflow Localization, language versions run directly on Webflow hosting, without an additional service in between. What that meant during PHP2Shell is covered in our article Webflow and PHP2Shell: Why Webflow Websites Are Not Affected.
Want to find out which services your website depends on and whether PHP is still running anywhere? Book a short call with us. How we set up and maintain Weglot in client projects is covered on our Weglot agency page, and more about Webflow on our Webflow agency page.
Sources
As of October 23, 2026. The screenshots in this article show the date and time they were captured, the email shows the time it was received. The situation is still developing, and the official sources always take precedence. This article does not replace a security review of your specific setup.
Weglot
- Email from Weglot's Customer Success team to marketer UX, October 22, 2026, 5:44 pm CEST (on file)
- Weglot: "How Weglot technically works"
- Weglot Help Center: "How do I set up my DNS?"
- Weglot status page: status.weglot.com, no entry on PHP2Shell as of October 23, 2026
- WordPress.org: "Translate WordPress with Weglot 2.0 – Multilingual AI Translation"
- Packagist: weglot/weglot-php
PHP and Webflow
- PHP project, php.net: "Security advisory: Critical remote code execution vulnerabilities, update now", October 21, 2026
- PHP project, php.net: "Informational advisory: Session upload progress", October 23, 2026
- Webflow Trust Center: "PHP2SHELL vulnerabilities statement", October 21, 2026
FAQ
Is Weglot affected by PHP2Shell?
Parts of Weglot's infrastructure run on PHP. According to Weglot, its services have been running on patched PHP versions since around 7 pm CEST on October 21, 2026, with additional firewall rules in place from around 3 pm. Weglot confirmed this to us by email on October 22.
Does Weglot run on PHP?
Partly. Weglot confirmed to us that parts of its infrastructure run on PHP. The Weglot WordPress plugin is also PHP code itself and runs on your own server.
Do I need to do anything about PHP2Shell as a Weglot customer?
According to Weglot, everything has been done on Weglot's servers. What you need to check is your own server: always on WordPress with the Weglot plugin, and with subdomains or subdirectories your original site, if it runs on PHP.
Does updating the Weglot plugin protect against PHP2Shell?
No. The vulnerability is in PHP itself, not in the plugin. Your hosting provider has to update PHP on your server to 8.2.35, 8.3.36, 8.4.27, 8.5.12 or later.
Is Weglot on Webflow affected by PHP2Shell?
Webflow itself is not affected, which Webflow has confirmed officially. With subdomains or subdirectories, the language versions are delivered by Weglot's reverse proxy. According to Weglot, its services were patched on October 21.